
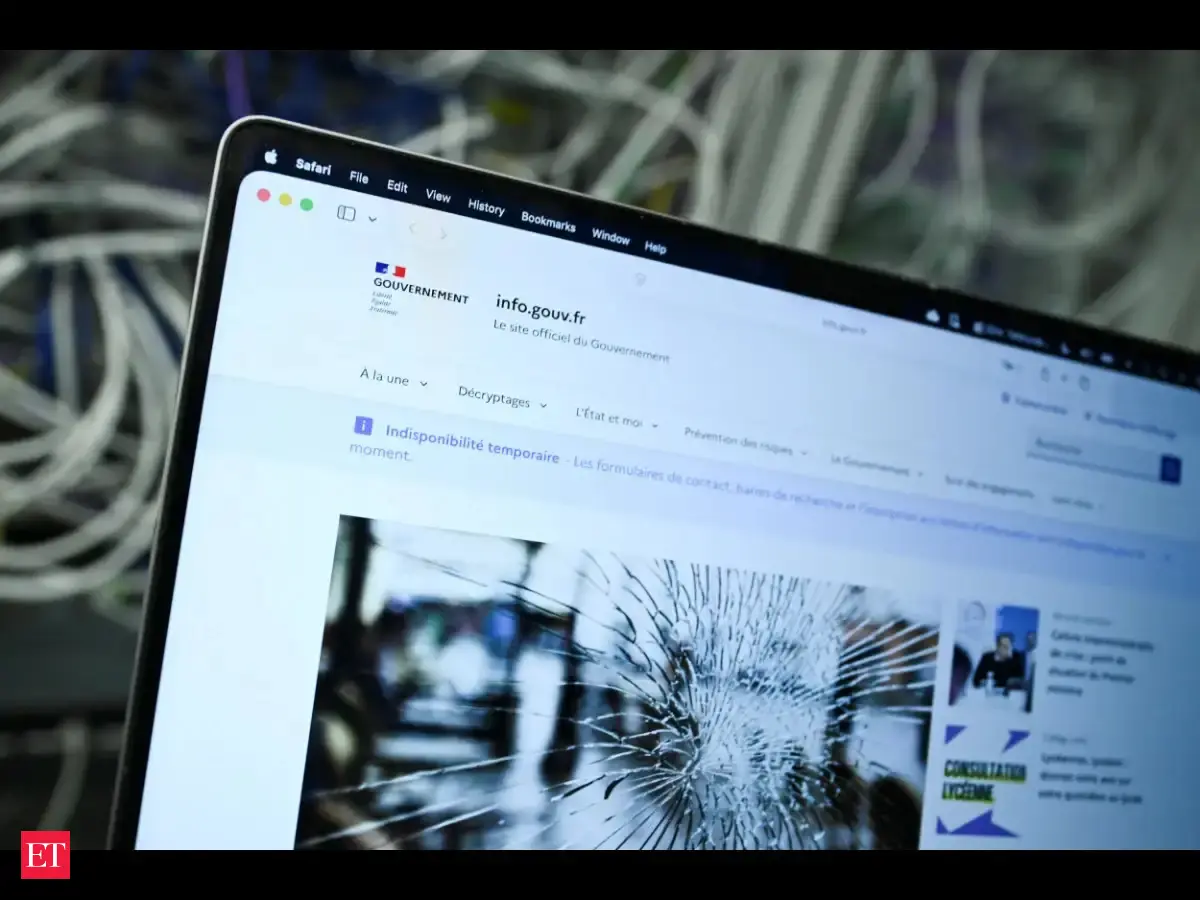
Photo via economictimes.indiatimes.com
AI uncovers critical PHP flaws affecting 70% of internet
Two critical vulnerabilities in the PHP programming language, discovered using AI, forced government websites offline globally on October 21.
What happened
Two critical vulnerabilities in PHP, the programming language behind roughly 70% of the internet, were disclosed on October 21 after being uncovered through AI-assisted research by multiple security teams. The flaws, tracked as CVE-2026-109618 and CVE-2026-109619 and rated 9.2 out of 10 in severity, allow unauthenticated attackers to execute code remotely on affected servers without logging in.
The vulnerabilities were discovered independently by Wiz Research (starting August 19), Calif (with OpenAI's GPT-5.6 Sol model), and others using AI tools that could identify exploitable weaknesses in code that had remained hidden for over 14 years. OpenAI coordinated a two-month "Patch the Planet" coalition with researchers, government agencies, and infrastructure providers to prepare fixes before public disclosure. The PHP Foundation released patched versions on October 21 at approximately 13:45 UTC.
In response, government websites in the Netherlands, Finland, France, Australia, Denmark, and Canada went offline temporarily as a precaution before installing patches. The Dutch cybersecurity agency itself went offline, as did Wikipedia and the Internet Archive. According to Censys data, approximately 1.5 million of 2.6 million hosts running PHP lack access to fixed versions.
Cybersecurity agencies worldwide—including the FBI, NSA, and CERT-EU—urged organizations to update immediately or take systems offline until patches could be applied. The White House noted the discovery on October 16 and framed it as validation of American leadership in artificial intelligence. Early attacks exploiting the flaws were reported within hours of disclosure, with Cloudflare implementing firewall rules to block exploit attempts.
Chanakya's Move
OpenAI's orchestration of the PHP response represents a strategic move to establish itself as the responsible steward of AI-enabled security research. By leading a coordinated disclosure process and proposing a five-stage framework for future AI-discovered vulnerabilities, OpenAI is attempting to shape how frontier AI will be deployed in infrastructure defense—and by extension, to secure regulatory goodwill and market position. The White House's framing of this as a triumph of American "Super Intelligence" leadership signals that the Trump administration will use AI-enabled cybersecurity wins to justify continued large-scale AI investment and minimal regulatory constraints. The vulnerability illustrates both AI's value (finding 14-year-old exploitable flaws before criminals) and its danger (the same AI tools will accelerate attacker exploit development). Companies like Wiz (Google-owned) and Cloudflare demonstrated how quickly they could operationalize defensive measures pre-disclosure, but the race now hinges on whether 1.5 million unpatched hosts can update before organized attacks mature. The coordination succeeded in buying defenders a two-month window—whether that proves enough remains unclear.